Sumus Lab
A hacker terminal in your browser. Ten simulated labs, tools that answer like the real ones, and not a single packet leaving the page.
Watch the trailer

A capture-the-flag that teaches the fix
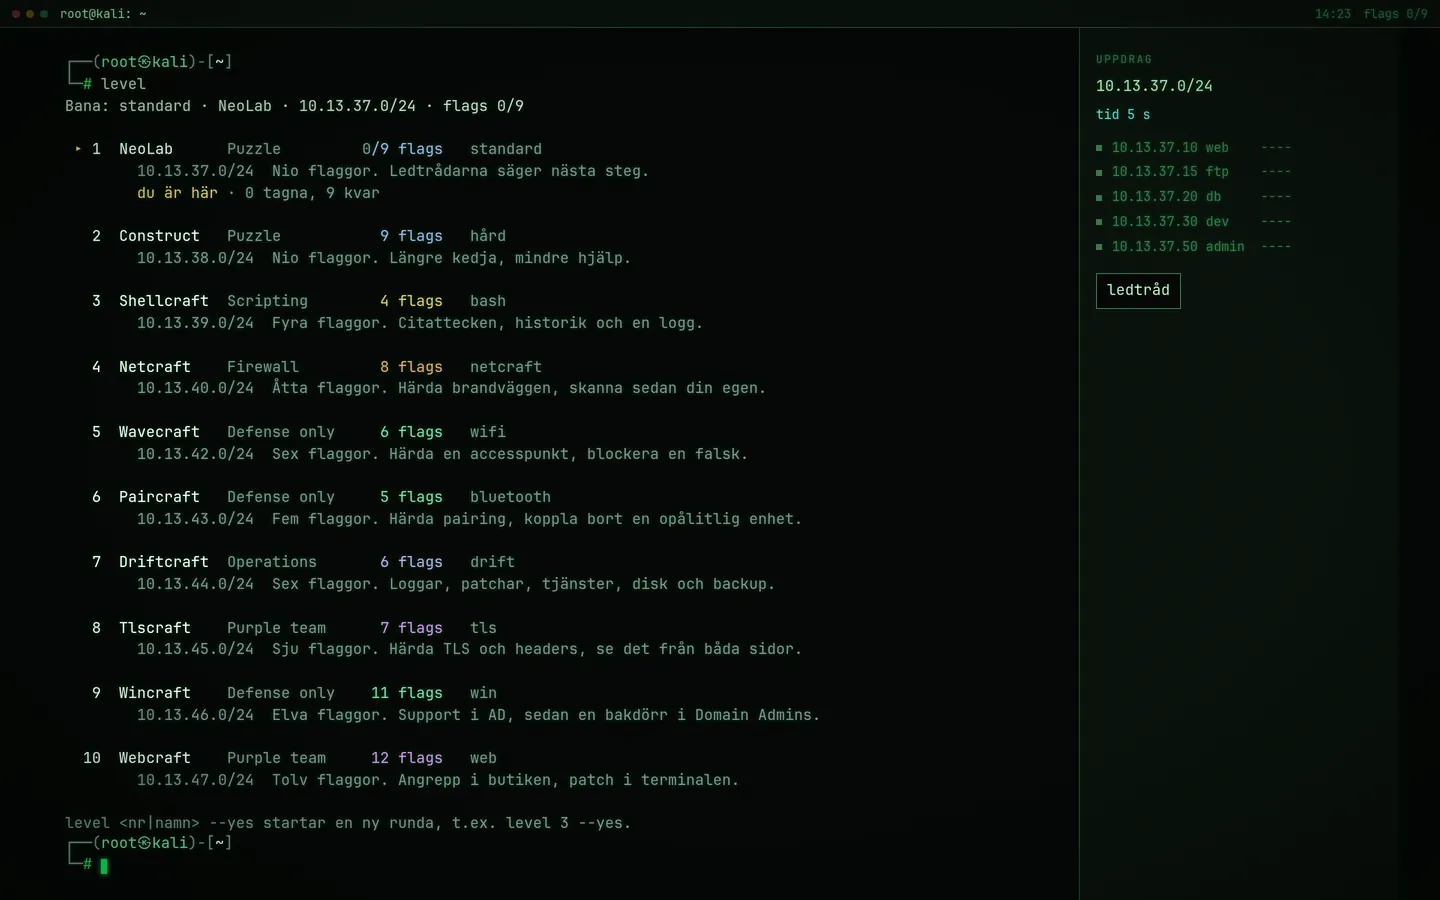
You sit at a Kali-style root prompt. Pick a lab and the clock starts. Every lab is its own fictional network with flags to find or controls to fix. mission points to the next step, and after each flag a short line explains how that hole gets closed.
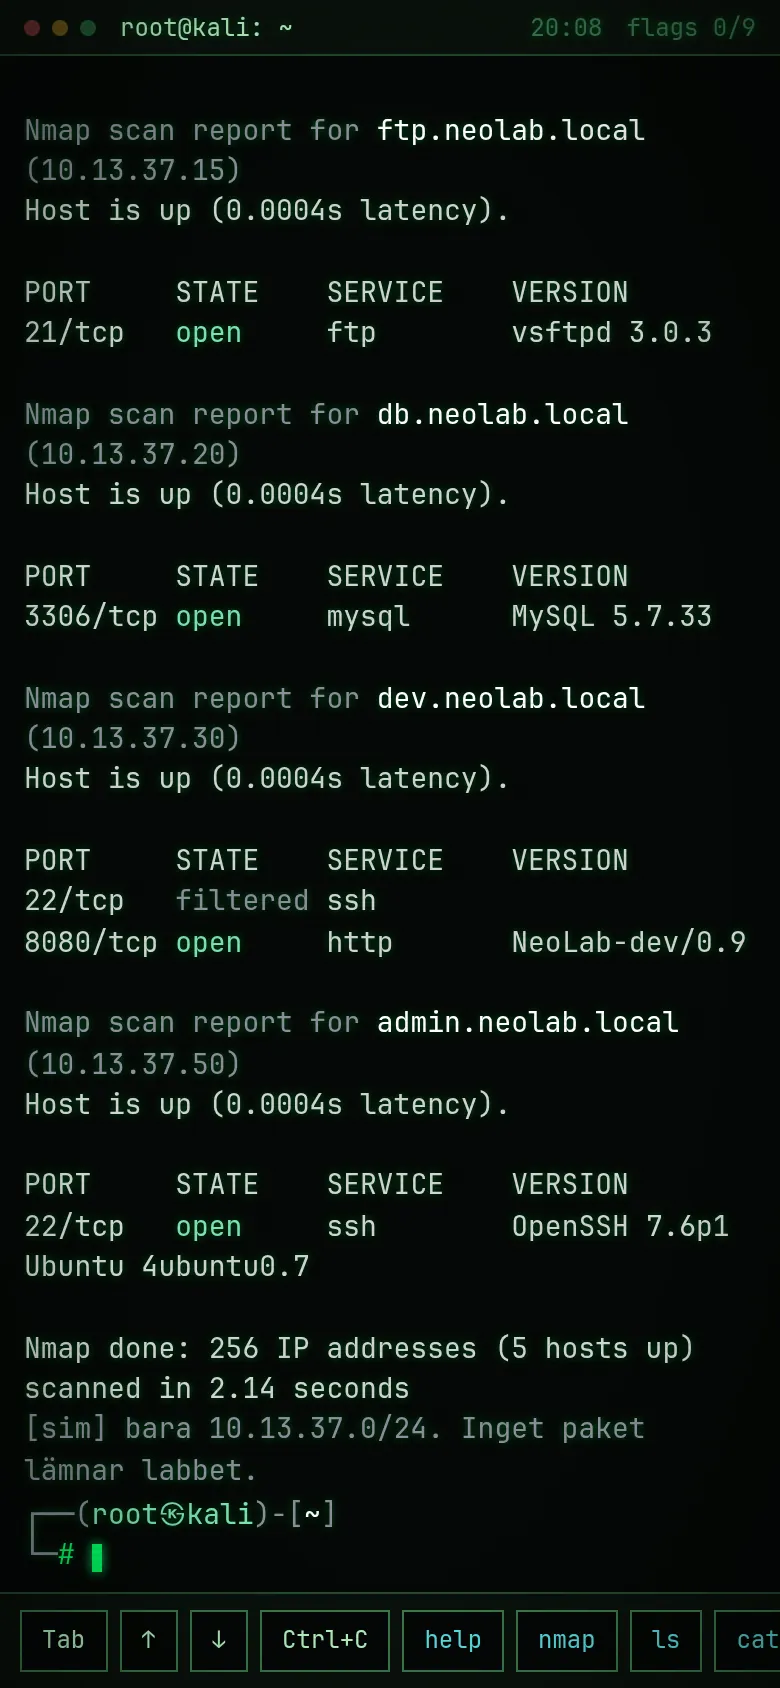
nmap, curl, ufw, apt, sed, nginx, sslscan and a PowerShell for Active Directory all answer the way the real tools would, but they are small models running in the page. In the defense labs, hint opens up to three levels, from a nudge to a full explanation.
Finish a lab and you can put an alias on the hall of fame. The time is measured on the server, from the moment the round starts until the last flag is in. No account and no email.
Tracks
NeoLab
PuzzleThe original chain: a small network with a web server, FTP, a database, a dev console and an admin box. Short hints tell you the next step.
Construct
PuzzleA second fictional network with a longer chain and shorter hints. The map only shows what your own box can see.
Shellcraft
ScriptingA workshop, not a break-in: fix shell scripts — shebang and execute bit, quoting a variable, keeping a secret out of the history, and finding the address with the most HTTP 401s in a log.
Netcraft
FirewallHarden the gateway with a simulated ufw, then switch to the attacker's box and scan the same rules from outside: open, filtered and closed come straight from your rules.
Wavecraft
Defense onlyHarden an access point — no TKIP, WPA3 SAE, protected management frames, no WPS, client isolation — and block a rogue access point that is missing from the inventory. No sniffing and no cracking.
Paircraft
Defense onlyHarden Bluetooth pairing — discoverability, Just Works, key size, address privacy — and disconnect an untrusted device. Only already-paired devices are listed; there is no scan for new ones.
Driftcraft
OperationsDay-to-day upkeep: pipe a log through grep, awk, sort and uniq, patch a package with apt, clean a leaked password out of a log, and fix a crashing service, a full disk and a broken cron job.
Tlscraft
Purple teamAfter an incident at an nginx web shop: see the weaknesses from the attacker's box with curl, sslscan and frametest, then fix the server — https redirect, HSTS, modern TLS only, strong ciphers, a valid certificate and security headers.
Wincraft
Defense onlyA simulated PowerShell on a fictional Active Directory domain. First support — a locked-out user, a wrong group, a computer in the wrong OU — then security: a backdoor admin, SMBv1, RDP with NLA, password policy and an unknown local admin.
Webcraft
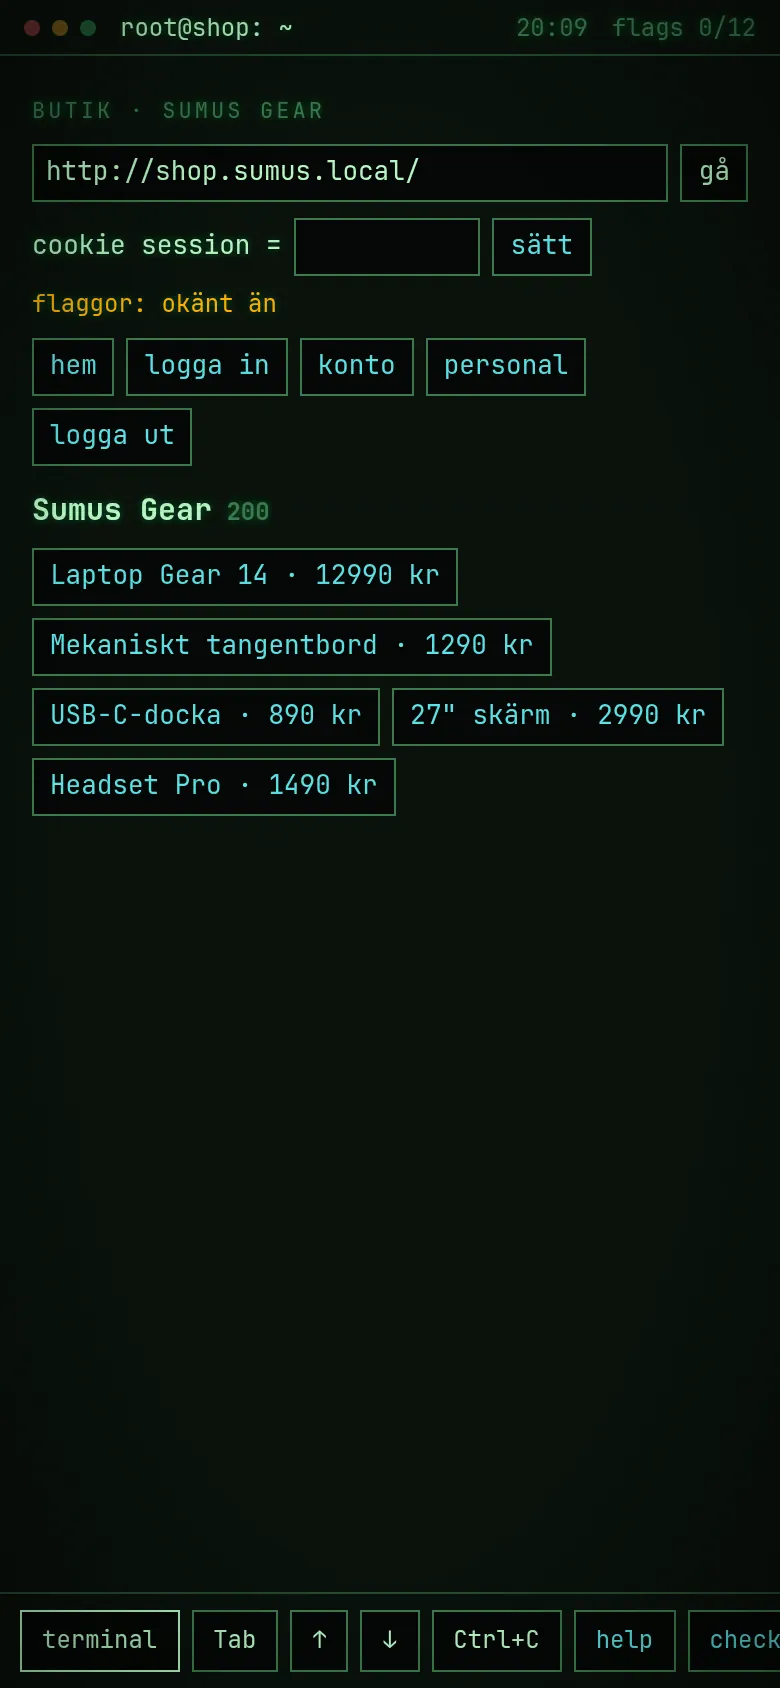
Purple teamSumus Gear, a fictional web shop in its own pane next to the terminal. Exploit classic web flaws in the shop or with curl, then fix the code and prove the same attack fails while normal use still works.
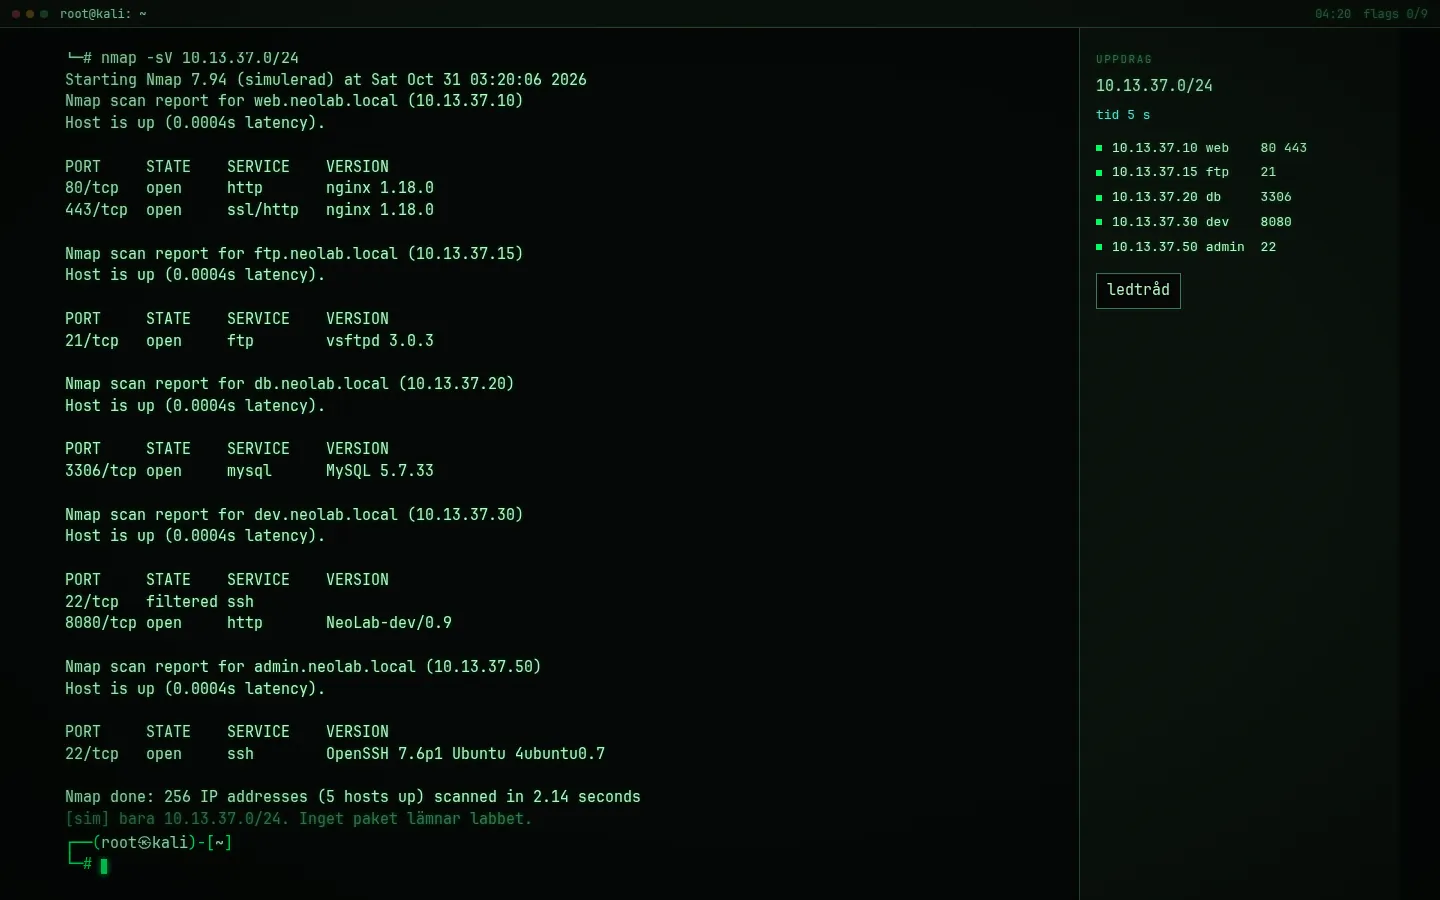
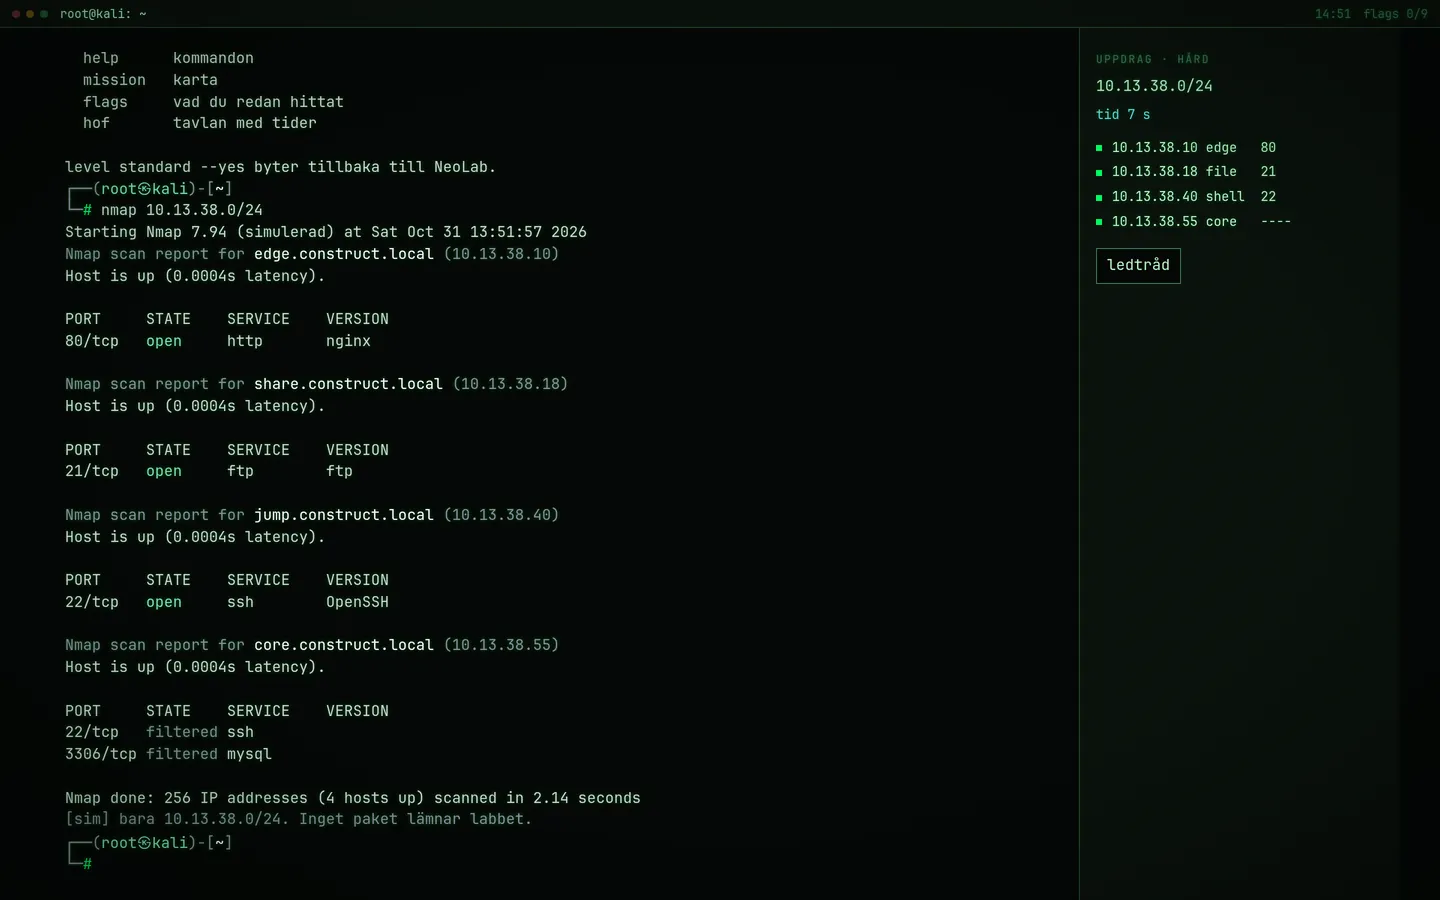
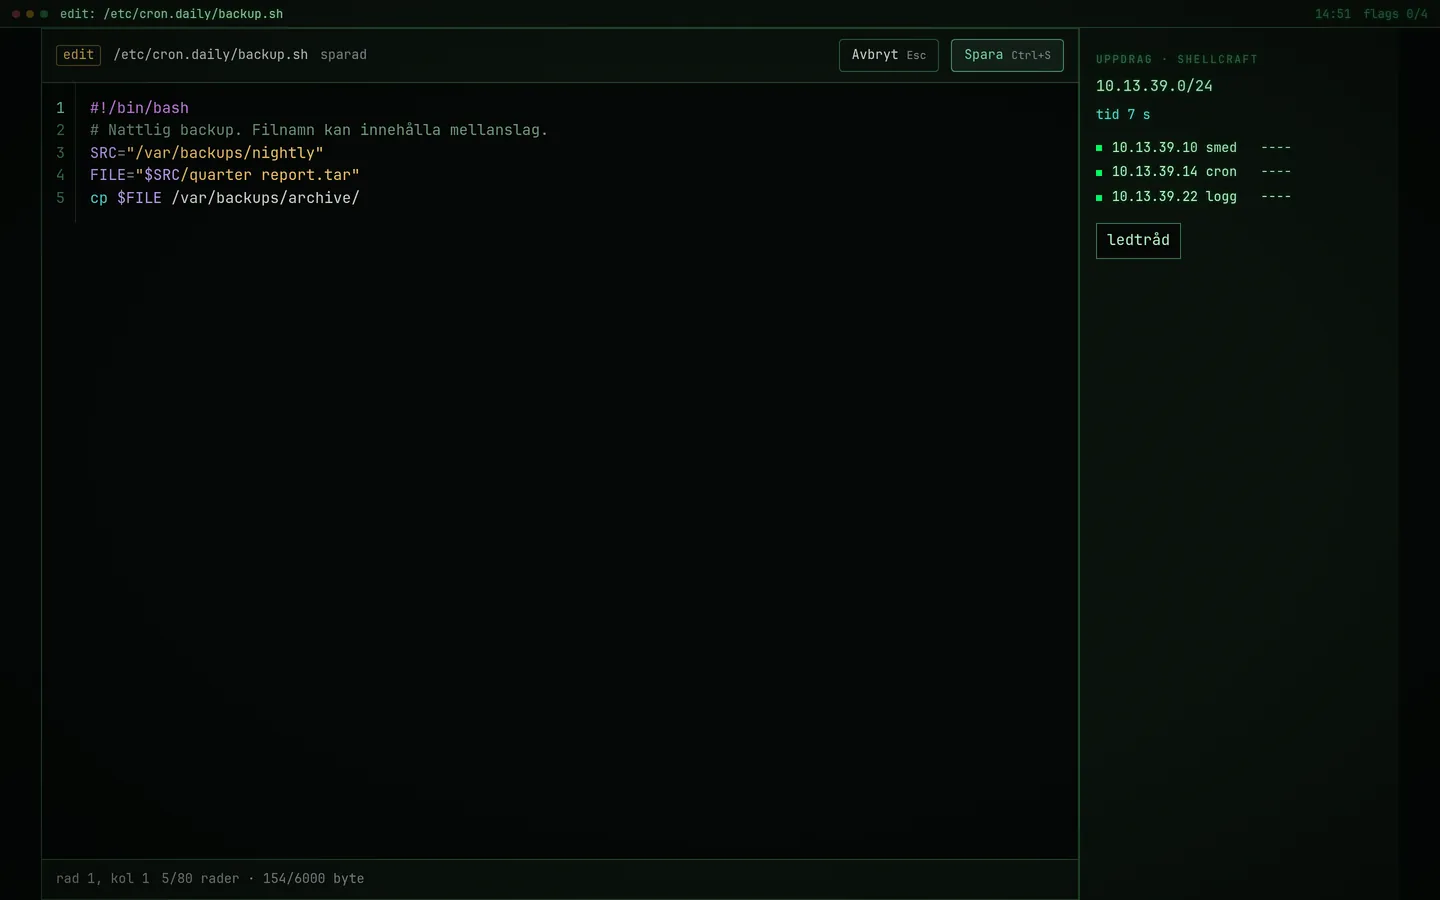
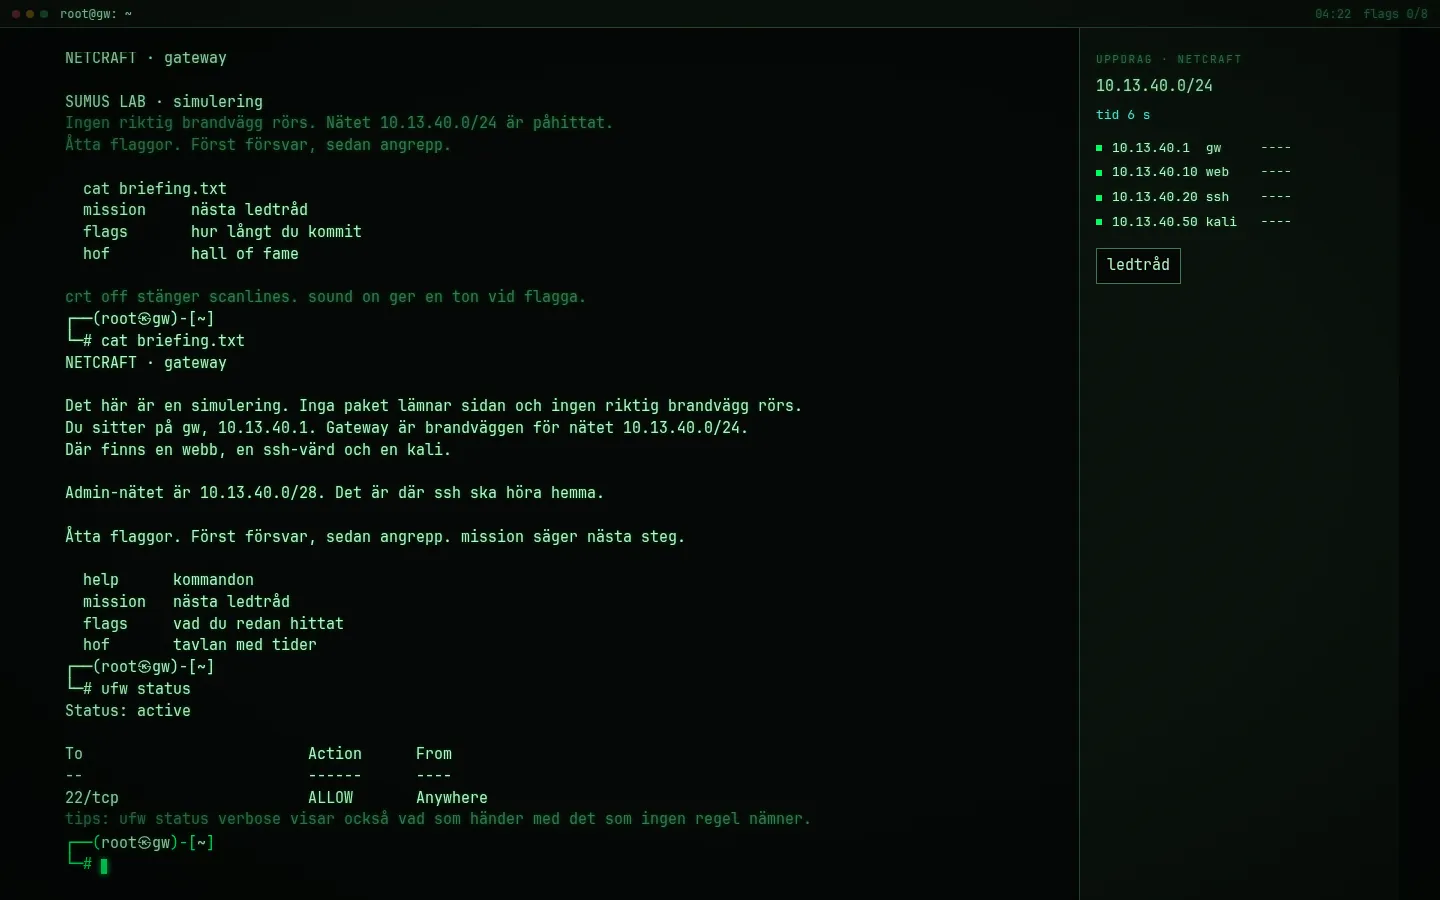
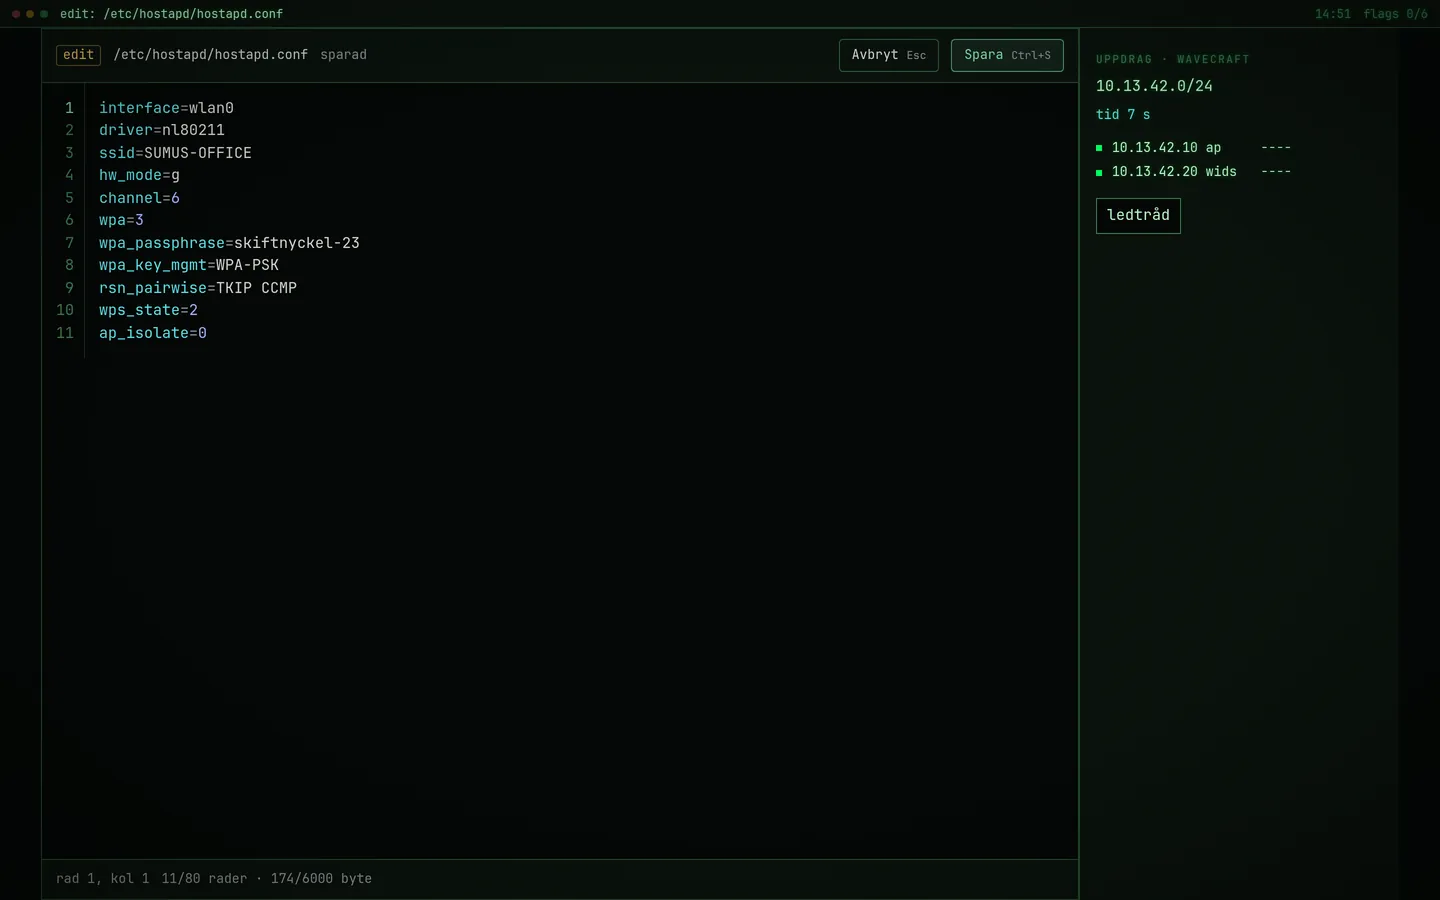
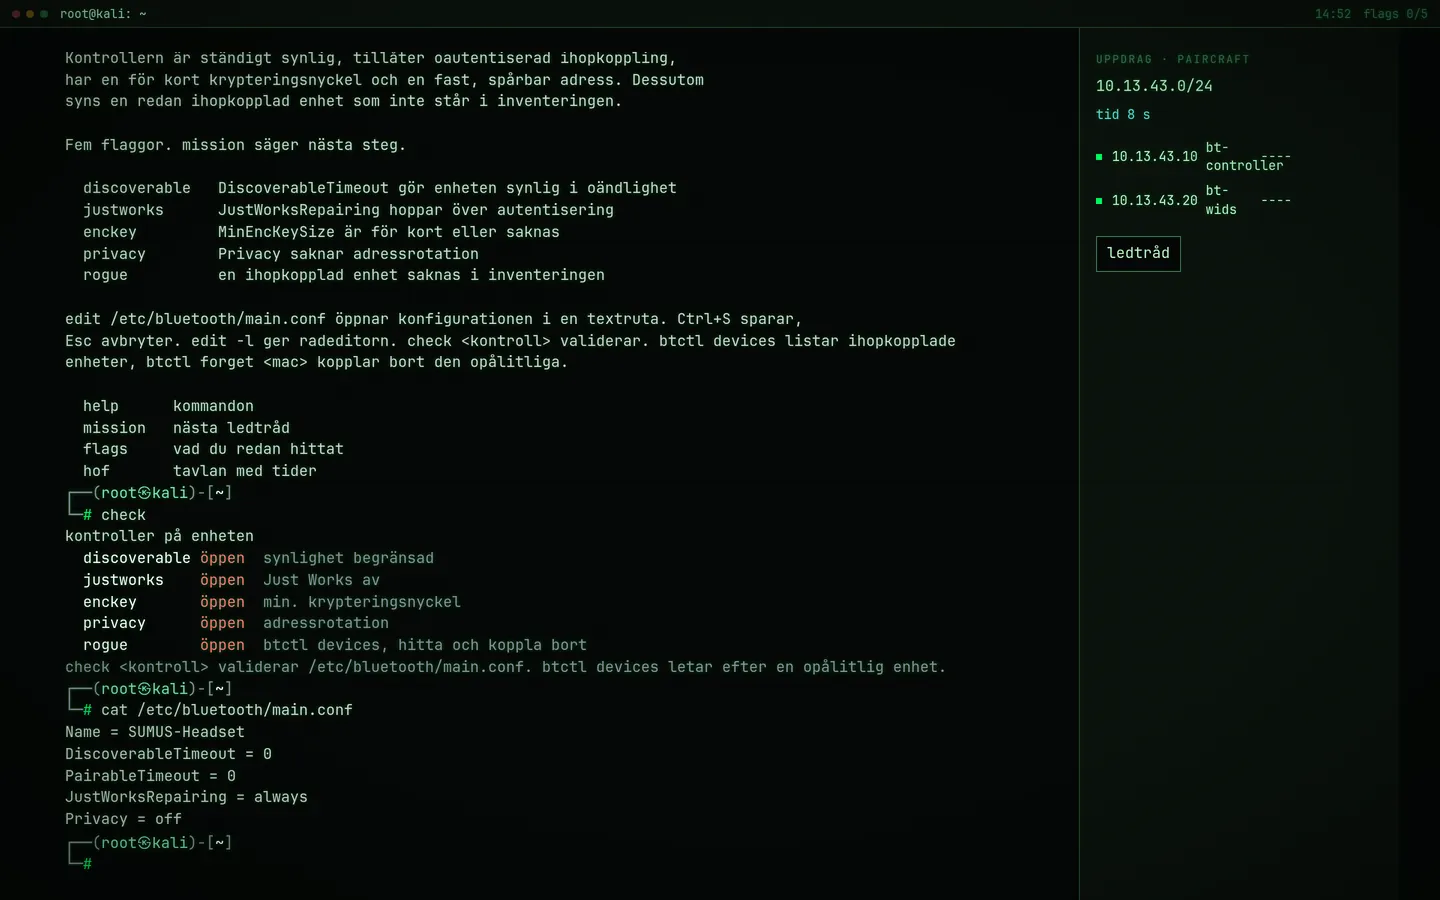
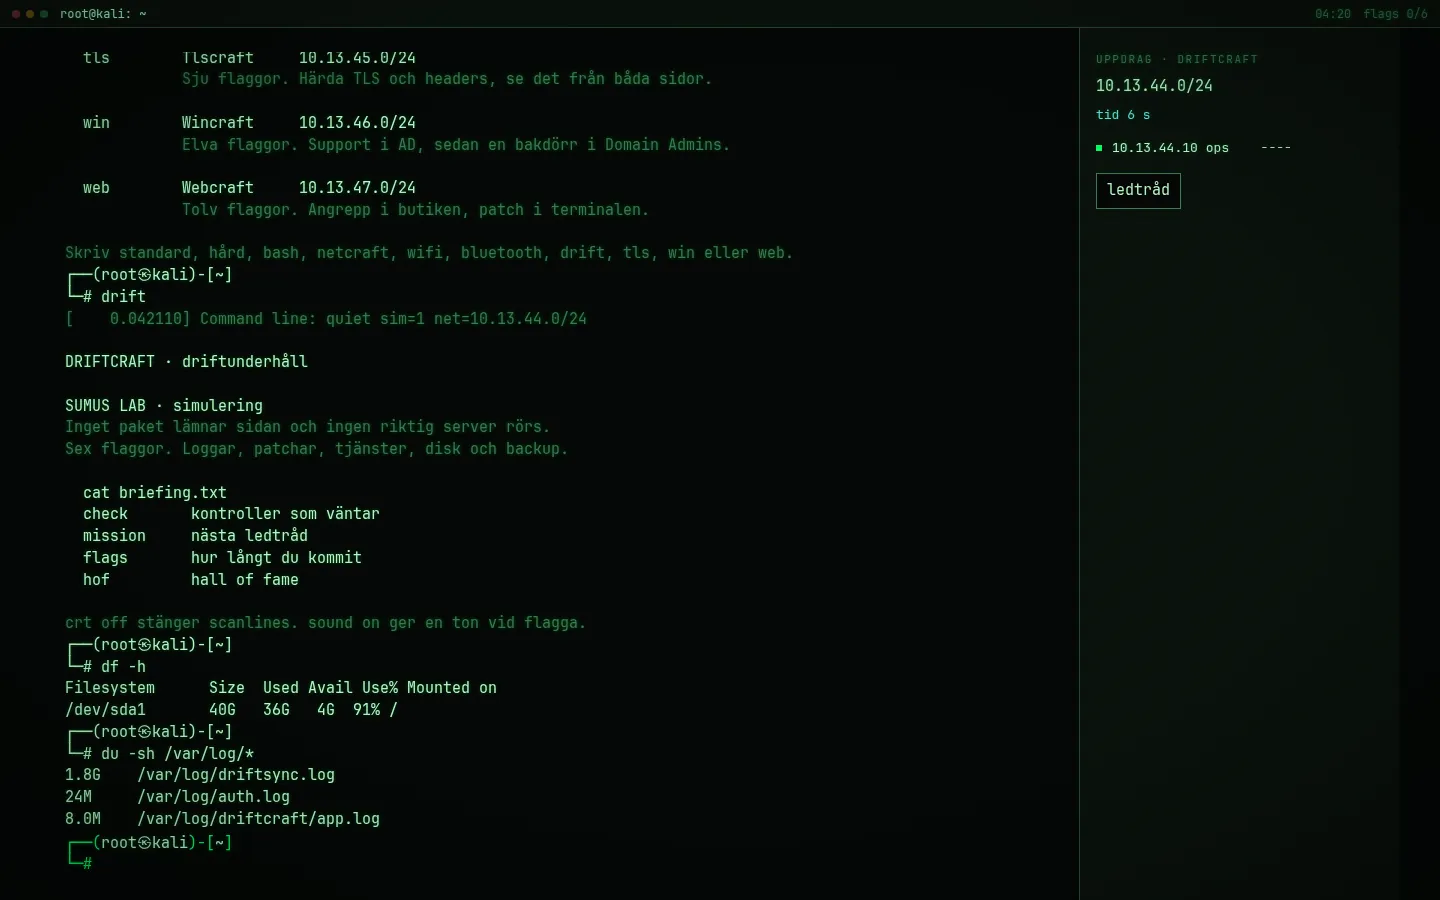
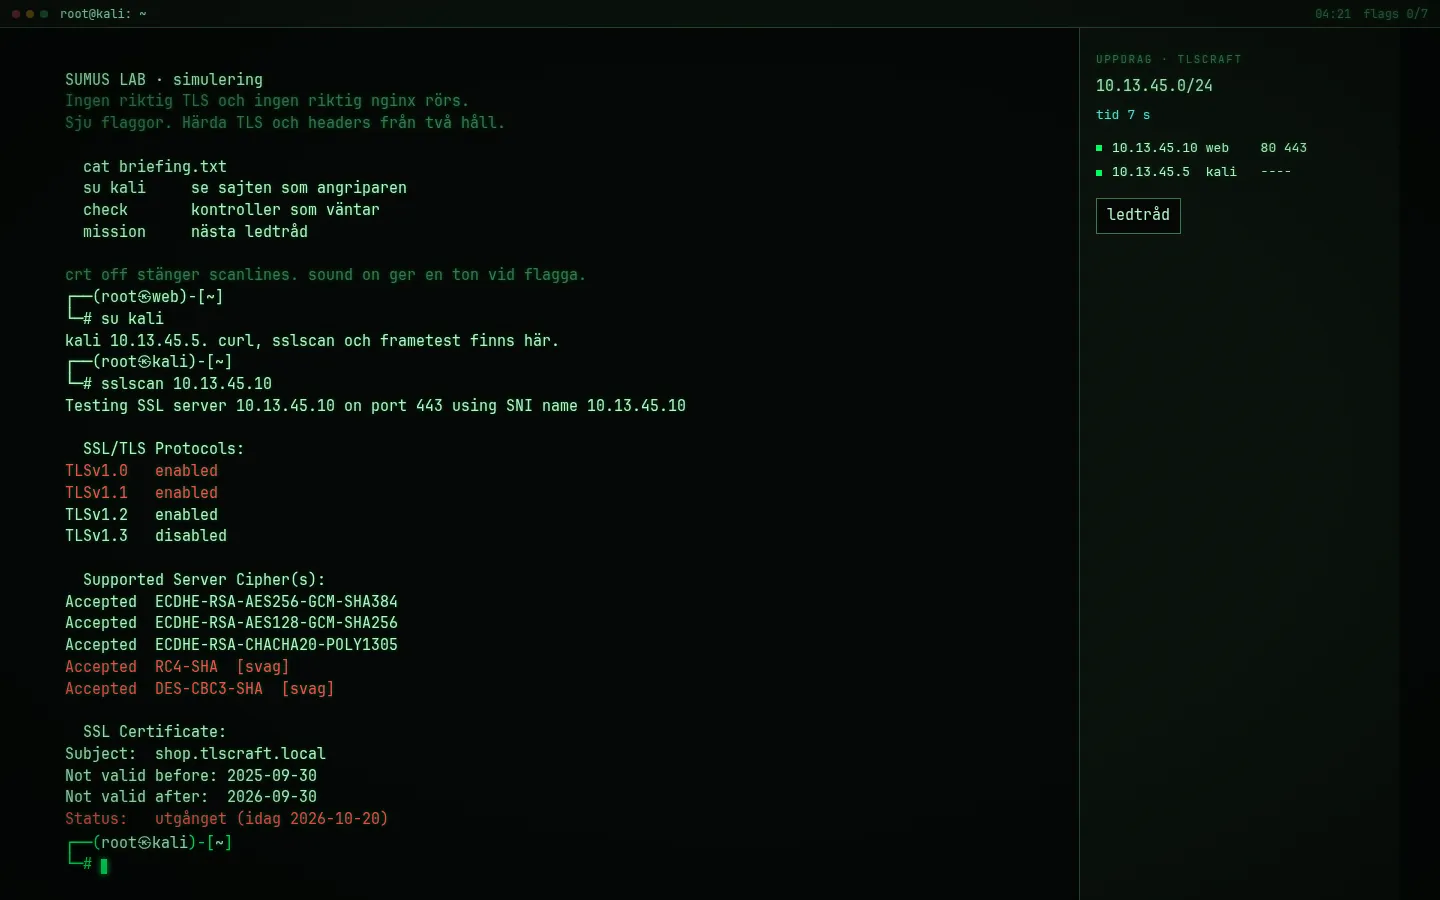
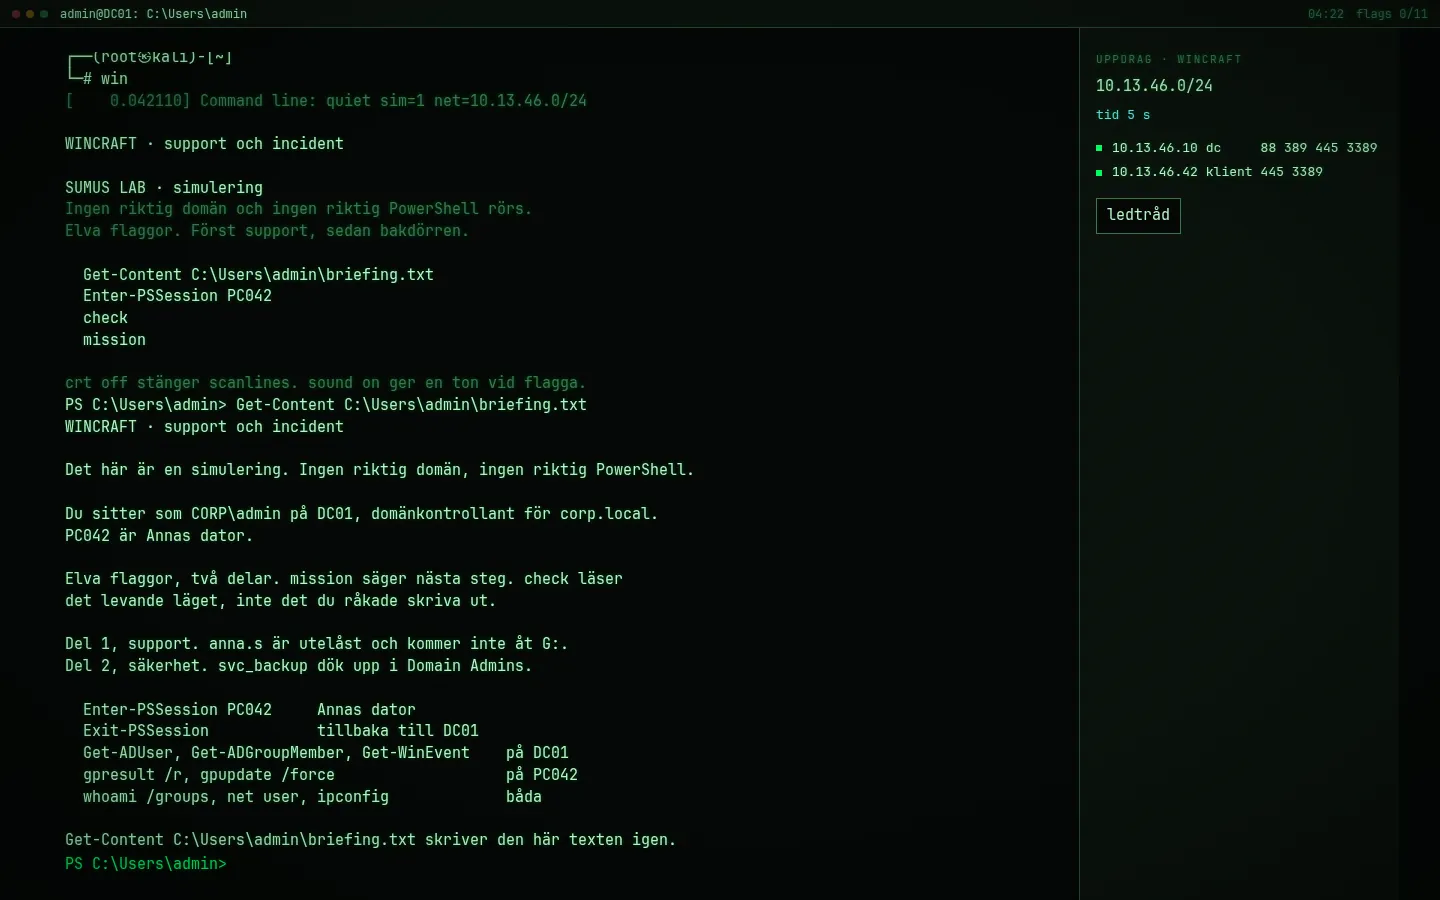
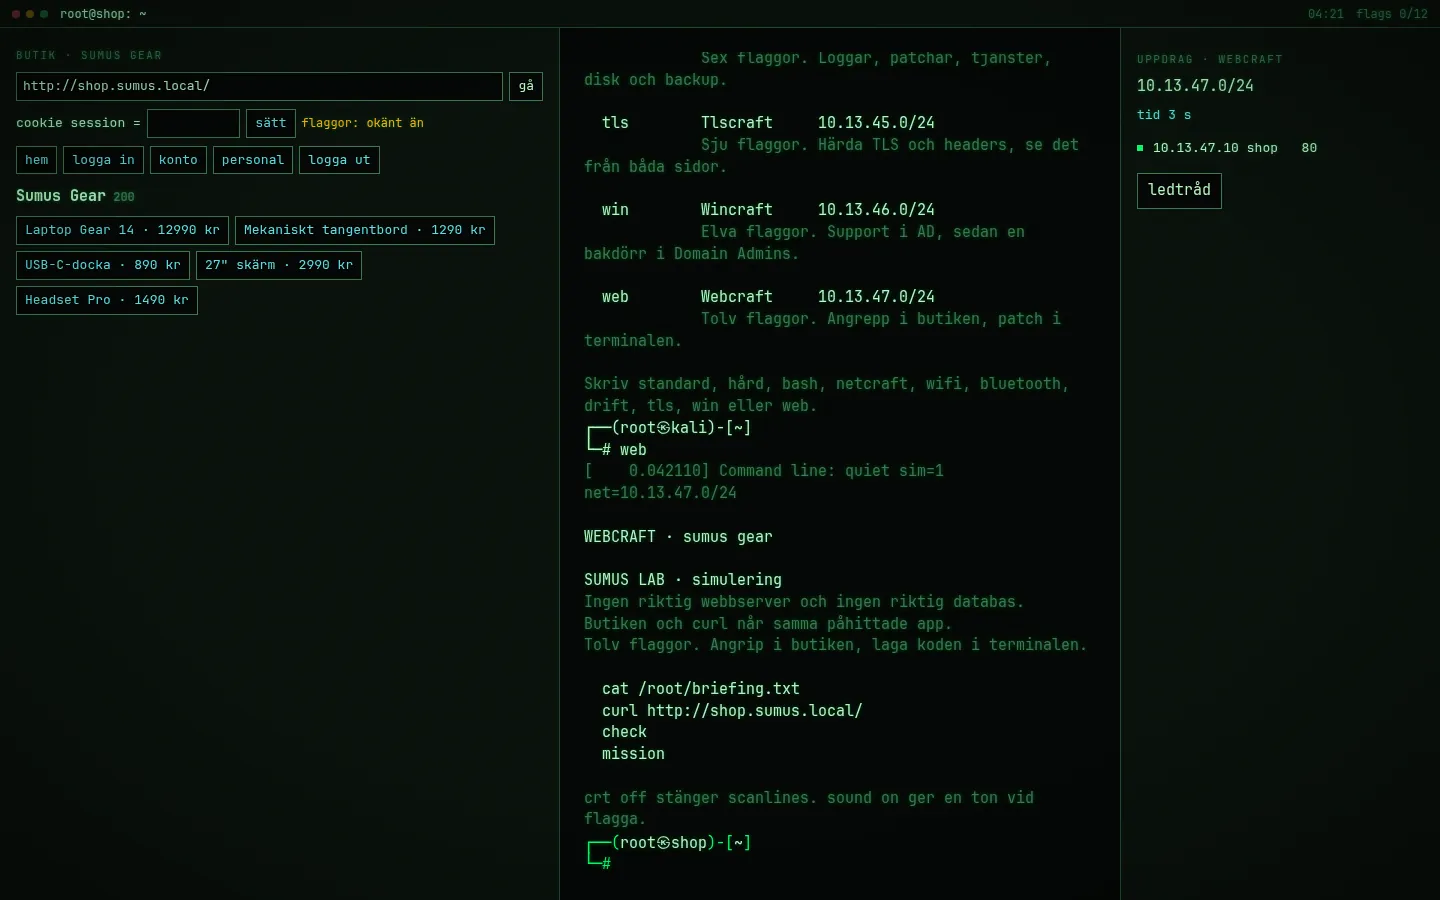
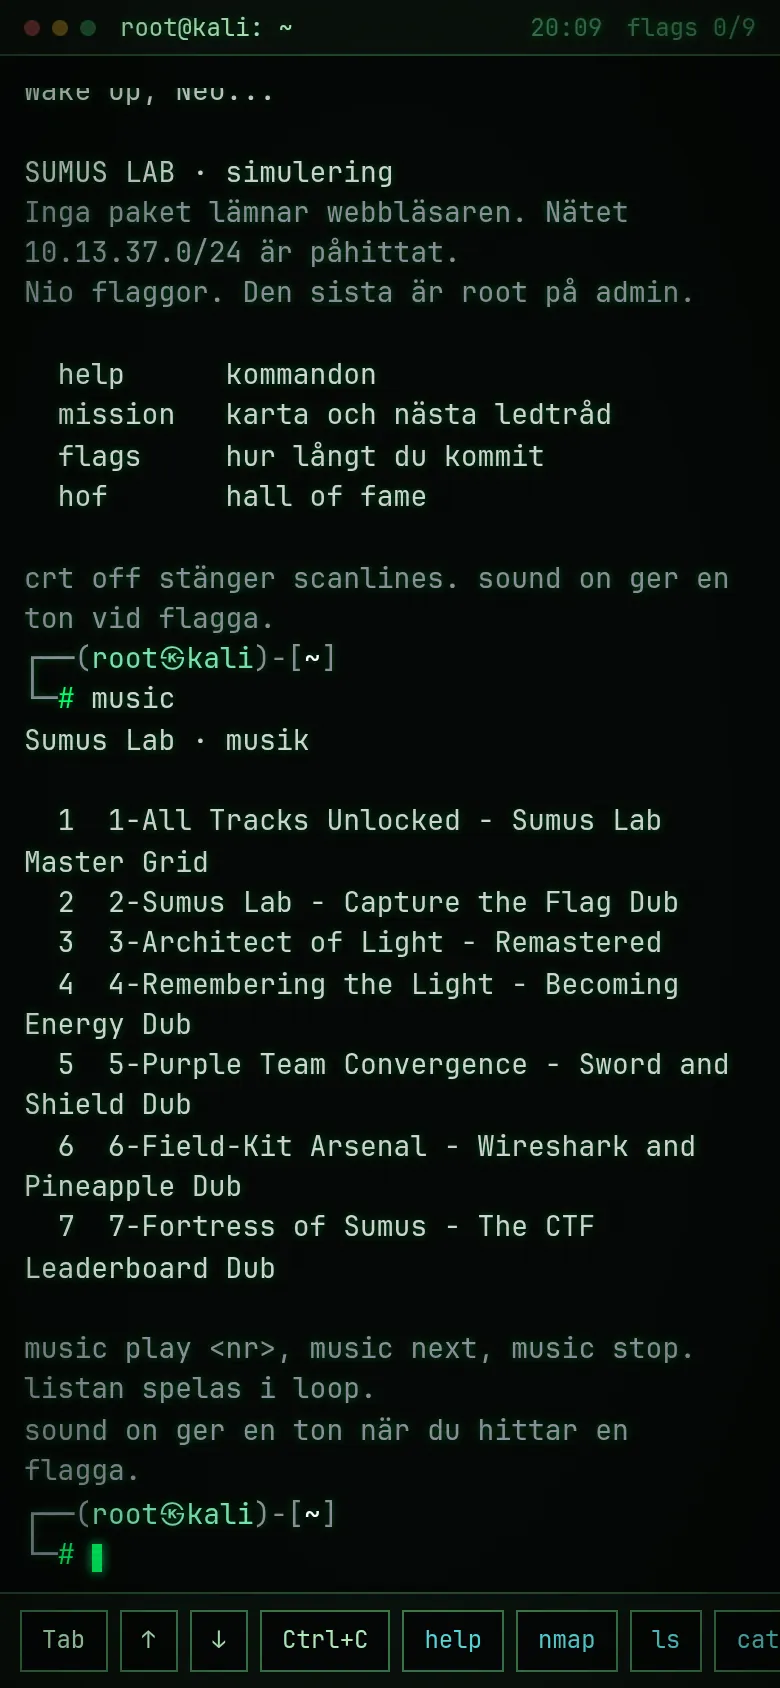
Screenshots show starting positions and first commands only, with no flags or solutions. Every address and host name in them is part of the simulation.
Attack and defense in the same lab
In Netcraft, Tlscraft and Webcraft you switch sides. Find the weakness from the attacker's box, fix it on the server, then run the same attack again and see it fail while normal use still works. The flags are for the defense as much as for the attack.
Wavecraft, Paircraft and Wincraft are defense only by design. There are no eavesdropping, handshake-capture or cracking tools, and Driftcraft is pure operations: logs, patches, services, disks and backups.
Works on a phone
Touch keys for Tab, arrows and Ctrl+C, shortcuts for common commands, a toggle between the web shop and the terminal, and the soundtrack with the music command.
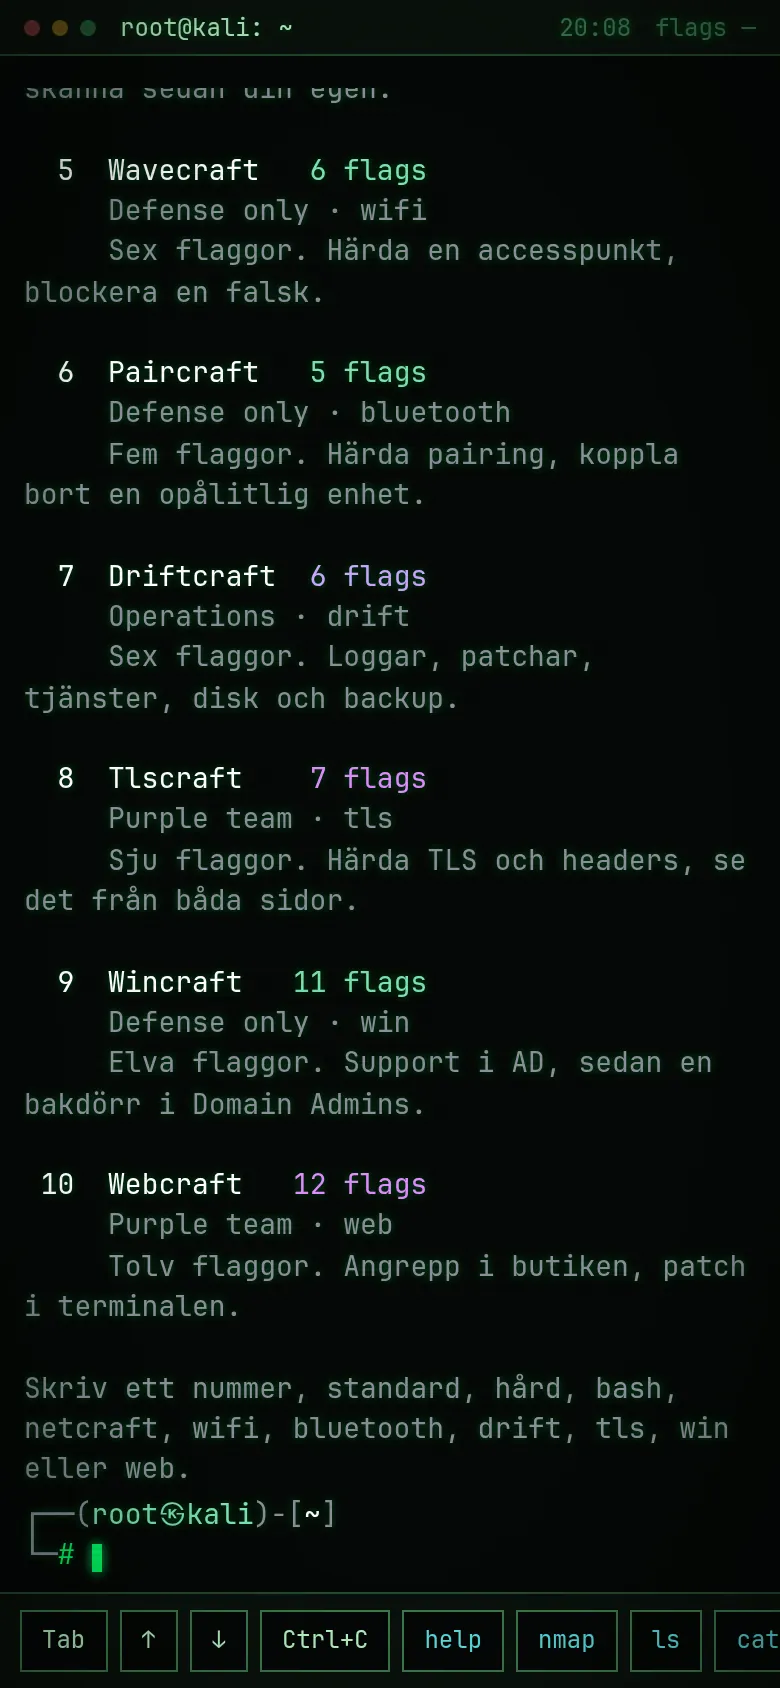
Built to be safe to play
- SimulatedThe tools are models inside the page. Nothing reaches a real network, radio, domain or server.
- Server-checkedFlags are checked on the server and are not in the JavaScript bundle. The clock is the server's.
- HardenedOne container for the static files and a small API: read-only root filesystem, non-root user, no npm at runtime, strict Content Security Policy.
- PrivateCompletion times in SQLite under an alias. No accounts, no email and no IP addresses stored. Rate limits slow down floods.

Public launch coming
Sumus Lab is still in development. It will open to the public at its own address once it is ready. Until then, this page is the tour.
All projects